
CVE-2026-77337: CakePHP Authentication Cookie Bypass - What It Means for Your Business and How to Respond
Introduction
CVE-2026-77337 is a critical authentication flaw in the CakePHP Authentication plugin, a widely used component for controlling access to web applications. If your organization operates a customer portal, internal dashboard, API, or e-commerce platform built with CakePHP, an attacker may be able to impersonate legitimate users without knowing their password. The issue can also consume server resources, potentially disrupting application availability. This post explains who is exposed, what the risk means operationally and reputationally, and the practical steps your team should take to contain and remediate it.
Background & History
GitHub published the maintainer advisory GHSA-h7xh-9h2x-2m37 on August 21, 2026, and the CVE record was published on August 24, 2026. The vulnerability affects the CakePHP Authentication plugin, specifically its CookieAuthenticator when it relies on unencrypted, forgeable legacy tokens.
The flaw is rated Critical, with a CVSS v3.1 base score of 10.0. It is classified as authentication bypass by spoofing and, in some configurations, uncontrolled resource allocation. Fixed releases are 2.11.2, 3.3.7, and 4.2.1; the advisory credits markstory as the publisher of the GitHub security advisory.
What This Means for Your Business
If your application uses the affected CakePHP Authentication versions and CookieAuthenticator with unencrypted cookies, an outside attacker may be able to create or alter a cookie that makes your application treat them as an authenticated user. That can expose customer records, financial data, internal documents, administrative functions, or any other information protected only by a login screen.github
The direct consequences can include unauthorized account access, fraudulent transactions, tampering with business records, and theft of sensitive customer data. Because the attack requires no password and no user interaction, a single exposed internet-facing application can become an entry point into broader business systems.github
There is also an availability concern. Crafted tokens may force expensive processing and contribute to CPU or memory exhaustion, which can slow or interrupt the application during an attack. For customer-facing services, that can translate into abandoned orders, missed service-level commitments, and increased support costs.
Finally, a confirmed compromise can create regulatory and contractual exposure. Organizations in the United States and Canada that handle personal information, payment data, health information, or regulated financial records may need to investigate, notify affected parties, and demonstrate that appropriate safeguards and incident-response processes were in place.github
Real-World Examples
Regional financial services provider: A regional bank uses a CakePHP-based customer portal for loan status, statements, and secure messaging. An attacker forges an authentication cookie, accesses another customer’s account, and views financial documents. The institution faces fraud investigations, customer notification costs, and heightened regulatory scrutiny.github
Mid-market healthcare organization: A healthcare provider operates a patient scheduling and records portal built on CakePHP. Unauthorized access to patient appointments or demographic information could compromise privacy obligations and force a costly breach assessment, even if clinical systems remain unaffected.github
E-commerce company: An online retailer’s account area allows customers to store addresses, payment preferences, and order history. A forged cookie could let an attacker change account details, view orders, or abuse loyalty benefits, resulting in chargebacks, support escalations, and lost customer trust.github
SaaS provider: A business software vendor hosts multi-tenant dashboards for its clients. Authentication bypass in one application could expose tenant data across customers, triggering contractual breach notifications, customer attrition, and emergency remediation work across hosted environments.github
Am I Affected?
- You use the
cakephp/authenticationComposer package in a CakePHP or PSR-7-based application. - You run version 2.11.1 or earlier, version 3.0.0 through 3.3.6, or version 4.0.0 through 4.2.0.
- Your application configures
CookieAuthenticatorfor login or session persistence.github - The authentication cookie is not encrypted, meaning the application does not use
EncryptedCookieMiddlewarefor theCookieAuthcookie or your custom cookie name.github - You have not upgraded to version 2.11.2, 3.3.7, or 4.2.1.
- You allow legacy authentication tokens, rather than disabling them with
legacyTokens = false.github
Key Takeaways
- CVE-2026-77337 is a critical authentication bypass in affected versions of the CakePHP Authentication plugin.
- The highest-risk configuration uses
CookieAuthenticatorwith unencrypted, forgeable legacy cookies.github - Successful exploitation can expose customer or business data, enable account impersonation, and disrupt service through resource exhaustion.
- Organizations handling regulated or sensitive information should treat any suspected exploitation as a potential data-security incident.github
- The vendor has released fixed versions: 2.11.2, 3.3.7, and 4.2.1.
Call to Action
If you operate CakePHP applications, do not wait for suspicious activity to confirm your exposure. IntegSec can assess your authentication configuration, verify whether legacy cookies remain enabled, test for exploitation paths, and help prioritize remediation across your web estate. Visit https://integsec.com to schedule a penetration test and strengthen your organization’s cybersecurity posture.
Technical Appendix
A — Technical Analysis
CVE-2026-77337 affects the CookieAuthenticator component of the cakephp/authentication package when authentication cookies use unencrypted, forgeable legacy token data. An attacker can supply a crafted cookie over HTTP, causing the application to accept spoofed identity information and bypass authentication.
The attack vector is network-based, with low attack complexity, no required privileges, no user interaction, and a changed security scope. The vendor-assigned CVSS v3.1 vector is CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:N, producing a base score of 10.0. The advisory also identifies potential CPU or memory exhaustion through forged tokens, mapped to CWE-770, alongside CWE-290.github
NVD lists affected ranges as versions before 2.11.2, 3.0.0 through 3.3.6, and 4.0.0 through 4.2.0. Patched releases are 2.11.2, 3.3.7, and 4.2.1. The official advisory is GHSA-h7xh-9h2x-2m37, and NVD provides the canonical CVE reference at https://nvd.nist.gov/vuln/detail/CVE-2026-77337.
B — Detection & Verification
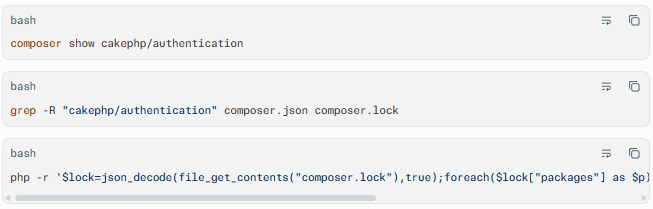
Version enumeration:
Configuration checks:

Log indicators: Review application and web-server logs for unusual CookieAuth or custom authentication-cookie values, repeated authentication successes without corresponding login events, and requests containing malformed or unusually large cookie payloads.github
Behavioral anomalies: Look for account access from unfamiliar IP addresses or user agents, access to records without a preceding password authentication event, and spikes in CPU or memory use coinciding with cookie-bearing requests.
Network exploitation indicators: Monitor for high volumes of requests carrying authentication cookies, especially requests with unexpected token length, encoding, or structure. Correlate these requests with authentication bypass attempts and resource-consumption alerts.github
C — Mitigation & Remediation
- Immediate (0–24h): Inventory all CakePHP and PSR-7 applications for
cakephp/authentication. Identify internet-facing systems running affected versions and determine whetherCookieAuthenticatoris enabled. - Immediate (0–24h): For systems that cannot patch immediately, enable
EncryptedCookieMiddlewareforCookieAuthor the application’s configured authentication-cookie name. This is the vendor-identified workaround for unencrypted authentication cookies.github - Short-term (1–7d): Upgrade
cakephp/authenticationto 2.11.2, 3.3.7, or 4.2.1, matching the application’s major version line. Test authentication, password reset, session persistence, and role-based access before production deployment. - Short-term (1–7d): After confirming that compatibility is no longer required, set
legacyTokens = falsein theCookieAuthenticatorconfiguration. This disables backward compatibility with existing token data and reduces the chance that legacy forgeable tokens remain accepted.github - Long-term (ongoing): Encrypt authentication cookies by default, enforce secure cookie attributes, rotate application secrets after a suspected compromise, and add dependency scanning to the software supply chain. Include authentication-bypass tests in routine penetration tests and regression suites.
D — Best Practices
- Keep
cakephp/authenticationand all Composer dependencies on supported, patched versions. - Encrypt authentication cookies with
EncryptedCookieMiddleware; never rely on unencrypted client-controlled tokens for identity decisions.github - Disable legacy token compatibility once migrations and user-session requirements allow it.github
- Monitor authentication logs for access without a matching login event and for anomalous cookie structures.github
- Include authentication bypass, cookie-tampering, and resource-exhaustion cases in application security testing
Leave Comment