
CVE-2026-71362: Adobe Commerce Authorization Bug - What It Means for Your Business and How to Respond
Introduction
CVE-2026-71362 is a critical security vulnerability affecting Adobe Commerce, Adobe Commerce B2B, and Magento Open Source, platforms used by retailers, manufacturers, distributors, and other organizations to operate customer-facing digital commerce. The issue can allow an external attacker to obtain elevated access to sensitive application resources without needing a user to click a link, open a file, or otherwise participate.
For organizations across the United States and Canada, this matters because an online storefront is not simply a sales channel. It is often connected to customer records, order workflows, inventory systems, payment services, marketing platforms, and business operations. A security weakness in that environment can create operational disruption and put trust, contractual obligations, and compliance commitments at risk.
This article explains the vulnerability in business terms, outlines practical exposure indicators, and provides response priorities. A technical appendix offers security and information technology teams guidance for verification, remediation, and longer-term hardening. Adobe has issued updates, and public-sector advisories report that the vulnerability has been exploited in the wild.
Background & History
Adobe published Security Bulletin APSB26-92 on August 11, 2026, covering CVE-2026-71362 in Adobe Commerce, Adobe Commerce B2B, and Magento Open Source. The issue was reported to Adobe by security researcher 0x0.eth, also known as 0x0doteth. It is categorized as an incorrect authorization vulnerability, meaning the platform can fail to enforce the access limits that should prevent unauthorized parties from reaching protected functions or resources.
Adobe assigned the vulnerability a Critical severity rating with a Common Vulnerability Scoring System score of 9.1 out of 10. The National Vulnerability Database published the record on August 11, 2026, and identifies the weakness as CWE-863, Incorrect Authorization.
The timeline became more urgent in September. The Canadian Centre for Cyber Security reported open-source indications of exploitation in the wild, and stated that the U.S. Cybersecurity and Infrastructure Security Agency added CVE-2026-71362 to its Known Exploited Vulnerabilities catalog on September 24, 2026. That progression means affected organizations should treat remediation as a near-term business priority, not a routine maintenance item.
What This Means for Your Business
If your organization operates an affected Adobe Commerce or Magento environment, this vulnerability could enable an attacker to gain access beyond what they should be allowed to have. In practical terms, elevated access may expose business-sensitive functions and data that support your online operations. Because exploitation does not require customer or employee interaction, awareness training alone does not address the immediate risk.
The operational impact can include disruption to online ordering, unexpected changes to store configuration, fraudulent activity, and emergency investigation work during high-revenue periods. If your storefront connects to customer data, loyalty programs, business-to-business accounts, fulfillment partners, or financial systems, an incident can have effects beyond the web application itself.
For U.S. and Canadian businesses, the consequences may also include notification assessments, contractual review, payment-provider scrutiny, and questions from regulators or enterprise customers. Even when payment card data is handled by a third-party processor, exposed customer information, account details, order histories, or administrative capabilities can still create significant legal, commercial, and reputational exposure.
The business response should be proportionate but prompt: determine whether you operate an affected version, apply Adobe’s official security update, preserve appropriate evidence, and validate that the remediation worked. Do not assume a web application firewall, managed hosting provider, or cloud platform has already resolved the underlying application issue.
Real-World Examples
Regional Bank: A regional bank uses Adobe Commerce for branded merchandise, customer promotions, and event registration. An attacker who gains elevated access could alter storefront content or access information associated with customer orders, forcing the bank to suspend the service and begin a costly investigation. The organization may also face customer trust concerns because the incident occurred on a digital channel carrying its brand.
Mid-Market Manufacturer: A manufacturer uses Adobe Commerce B2B for dealer pricing, parts ordering, and account-specific product catalogs. Unauthorized elevated access could expose commercially sensitive pricing or disrupt purchasing workflows for distributors. The result could be delayed shipments, strained channel relationships, and lost revenue during a critical sales period.
Canadian Retailer: A multi-province retailer uses Magento Open Source for online sales and connects it to inventory, customer-support, and email-marketing tools. If the commerce platform is compromised, the retailer may need to investigate whether customer contact information or purchase histories were exposed. That can trigger privacy and notification reviews, along with public-facing communications that affect loyalty.
Small Direct-to-Consumer Brand: A growing online brand relies on a lean technology team and a managed hosting partner. A successful attack could require the company to take the storefront offline while it restores confidence in the environment. For a business dependent on daily online sales, even a short disruption can affect advertising efficiency, fulfillment planning, and customer retention.
Am I Affected?
- You are running Adobe Commerce version 2.4.4 through 2.4.9 and have not applied the corresponding August 2026 security release for your supported branch.
- You are running Adobe Commerce B2B version 1.3.3, 1.3.4, 1.4.2, 1.5.2, or 1.5.3 and remain on the July 2026 security release or an earlier release.
- You are running Magento Open Source version 2.4.6, 2.4.7, 2.4.8, or 2.4.9 and have not installed the August 2026 security update.
- You operate more than one storefront, region, brand, cloud environment, or disaster-recovery instance and cannot confirm the version for each one.
- You use a hosting, managed service, or e-commerce development partner but do not have written confirmation that the Adobe update was applied and verified.
- You are using a current affected branch but have relied on older patch packages, customizations, or cloned environments that may not include the August 2026 fix.
- You are not affected by this specific CVE if every production and internet-accessible nonproduction instance is on Adobe’s listed August 2026 patched release or later, and you have verified the deployment.
Key Takeaways
- CVE-2026-71362 is a Critical authorization vulnerability in Adobe Commerce, Adobe Commerce B2B, and Magento Open Source with a vendor-assigned score of 9.1 out of 10.
- The vulnerability can be exploited remotely without authentication, administrative privileges, or user interaction, making externally accessible storefronts the priority for review.
- Public advisories indicate the flaw has been exploited in the wild and was added to the U.S. Known Exploited Vulnerabilities catalog in September 2026.
- Your primary response should be to identify affected instances, apply Adobe’s official August 2026 update for your supported release branch, and validate the deployment.
- Patching should be paired with incident-focused log review, access review, and independent validation when your commerce environment supports material revenue or sensitive customer operations.
Call to Action
A patch closes a known weakness, but it does not automatically establish whether your environment was exposed before remediation or whether other pathways remain. IntegSec helps organizations evaluate the security of customer-facing applications, identity controls, integrations, and cloud infrastructure through focused penetration testing and practical risk reduction.
If you operate Adobe Commerce or Magento in the United States or Canada, engage IntegSec to validate your exposure, test the effectiveness of your controls, and prioritize the changes that reduce business risk. Learn more or start a conversation at IntegSec.
Technical Appendix
A — Technical Analysis
CVE-2026-71362 is an incorrect authorization issue, classified as CWE-863, affecting Adobe Commerce, Adobe Commerce B2B, and Magento Open Source. Adobe’s advisory describes the impact as privilege escalation: an attacker can obtain elevated access to sensitive resources because authorization controls do not correctly enforce intended access restrictions.
Adobe assigned a CVSS v3.1 base score of 9.1 with vector CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:N. The vector indicates a network-reachable attack path with low attack complexity, no prerequisite privileges, and no user interaction. Confidentiality and integrity impacts are rated High, while availability impact is rated None.
The National Vulnerability Database record confirms the issue can permit elevated access to sensitive resources and notes that exploitation requires no user interaction. As of the available NVD record, the vulnerability is associated with Adobe Commerce product configurations and affected versions are addressed by the August 2026 releases.
B — Detection & Verification
Version enumeration should begin with each deployed Commerce codebase, including production, staging, preproduction, disaster recovery, and separately managed regional storefronts.
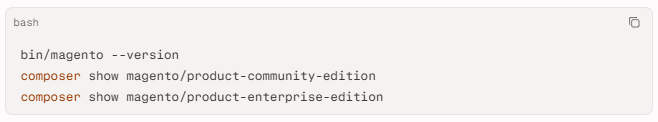
- Compare reported versions with Adobe’s patched August 2026 releases: Adobe Commerce 2.4.4-2026-aug through 2.4.9-2026-aug; Adobe Commerce B2B 1.3.3-2026-aug through 1.5.3-2026-aug; and Magento Open Source 2.4.6-2026-aug through 2.4.9-2026-aug.
- Configure vulnerability scanners to detect CVE-2026-71362 or identify installed product releases against Adobe’s affected-version matrix.
- Review web-server, application, reverse-proxy, and web application firewall logs for anomalous unauthenticated requests to application endpoints followed by unexpected privileged activity.
- Investigate unexplained administrative changes, new or modified privileged users, alterations to access-control settings, unexpected application configuration changes, and suspicious API activity.
- Correlate anomalous requests with authentication and administrative audit logs. A vulnerable version alone does not prove compromise, but public reporting of exploitation justifies targeted retrospective review.
C — Mitigation & Remediation
- Immediate (0–24h): Identify all internet-accessible Adobe Commerce, Adobe Commerce B2B, and Magento Open Source instances. Apply Adobe’s official APSB26-92 security update to the appropriate supported version branch as the first remediation action. Adobe lists August 2026 builds as the corrected releases and recommends updating to the newest available version.
- Immediate (0–24h): Preserve relevant web, application, authentication, administrative, and infrastructure logs before rotation. Review for unexpected privileged account activity, configuration changes, and suspicious requests during the exposure period. If indicators suggest compromise, initiate the organization’s incident-response process, isolate affected administration paths as appropriate, rotate credentials and secrets based on scope, and assess downstream integrations.
- Short-term (1–7d): Validate remediation in a controlled environment and production. Confirm deployed package versions, clear and rebuild application caches as required by the change procedure, conduct functional testing of checkout and business-to-business workflows, and perform authenticated testing of access controls. Review administrator and integration accounts for least privilege, stale accounts, and unauthorized modifications.
- Short-term (1–7d): If patching cannot occur immediately, reduce exposure as a temporary measure. Restrict administrative and sensitive application paths by network access controls, virtual private network access, allowlists, or identity-aware proxies where operationally feasible. Enable heightened web application firewall monitoring and rules only as compensating controls. These measures do not correct the authorization defect and must not replace vendor patching.
- Long-term (ongoing): Establish a documented emergency patch process for internet-facing business applications, including asset ownership, maintenance windows, rollback plans, log retention, and independent verification. Integrate continuous external attack-surface monitoring and periodic penetration testing so authorization weaknesses and exposed legacy instances are identified before they become urgent remediation events.
D — Best Practices
- Maintain a complete inventory of all Adobe Commerce and Magento instances, including test, staging, regional, backup, and disaster-recovery environments.
- Apply vendor security updates within defined service-level targets based on exposure and severity, with Critical internet-facing vulnerabilities receiving expedited treatment.
- Enforce least-privilege access for administrative users, service accounts, integrations, and deployment tooling, then review permissions after major releases.
- Centralize application, web-server, identity, and administrative audit logs so anomalous authorization behavior can be investigated across the full transaction path.
- Conduct recurring authenticated penetration tests that specifically assess authorization boundaries, privilege escalation paths, business-to-business account controls, and administrative workflows.
Leave Comment