
CVE-2026-62913: Microsoft Exchange Server Remote Code Execution Bug - What It Means for Your Business and How to Respond
Introduction
CVE-2026-62913 is a high-severity vulnerability in on-premises Microsoft Exchange Server that can allow an attacker with valid, low-level access to run code on a vulnerable server remotely. For organizations in the United States and Canada that continue to rely on Exchange for email, calendaring, internal communications, and business workflows, the issue deserves immediate executive attention.
Email remains a central business system and a high-value target. A compromise of an Exchange server can disrupt communications, expose sensitive correspondence, create a foothold for broader network intrusion, and complicate incident reporting obligations. This risk is especially relevant if your Exchange environment is internet-accessible or supports a large number of users, contractors, or service accounts.
This article explains the business significance of CVE-2026-62913, how to determine whether you may be affected, and the practical steps you should take. A technical appendix provides details for security and IT teams. Microsoft rates the issue 8.8 out of 10 under CVSS v3.1.
S1 — Background & History
Microsoft disclosed CVE-2026-62913 on August 11, 2026, and last updated its advisory on August 13. The vulnerability affects specific builds of Microsoft Exchange Server 2016, Exchange Server 2019, and Exchange Server Subscription Edition RTM. Microsoft credits Max Toor of Microsoft and Van1sher for reporting the issue.
The flaw is a heap-based buffer overflow, which in plain language means Exchange can mishandle certain data received over the network and potentially execute attacker-controlled instructions. Microsoft classifies the impact as remote code execution and assigns a CVSS v3.1 base score of 8.8, or High severity.
The important timeline is straightforward: Microsoft published the advisory and an official fix on August 11; subsequent August 12 and 13 revisions updated acknowledgements only, not the technical guidance. At publication, Microsoft stated that the vulnerability was not publicly disclosed, was not known to be exploited in the wild, and was considered less likely to be exploited. Those conditions can change, so patching should not wait for evidence of widespread exploitation.
S2 — What This Means for Your Business
For your business, CVE-2026-62913 is an email infrastructure risk with consequences beyond email. An attacker needs authenticated, low-level access, but no action from an employee is required once that access exists. In practice, compromised user credentials, a misused account, or a weakly governed service identity could make your Exchange environment a target.
Successful exploitation could give an intruder the ability to run code on the Exchange server. That may enable theft of mailbox content, manipulation of messages or server data, deployment of malicious tools, interruption of email service, or movement into connected systems. Microsoft’s CVSS assessment assigns high potential impact to confidentiality, integrity, and availability.
Operationally, email outages can delay customer support, invoicing, approvals, and coordination across offices. From a data perspective, mailboxes often contain customer information, employee records, contracts, credentials, and regulated communications. In the United States, a compromise may trigger contractual, state privacy, or sector-specific notification analysis. In Canada, it may also require evaluating obligations under applicable federal or provincial privacy laws and regulatory requirements.
Your reputational exposure can be equally significant. Customers and partners expect business email systems to be protected. A timely patch, disciplined access controls, and verified logging demonstrate reasonable cybersecurity governance. An unpatched server, particularly after an official vendor fix is available, is harder to defend in a post-incident review.
S3 — Real-World Examples
Regional bank: A regional bank uses on-premises Exchange for internal communications, customer-service coordination, and regulatory correspondence. If an attacker obtains a low-privilege account and exploits the vulnerability, the resulting server compromise could expose sensitive messages and disrupt time-critical operations. The bank would need to assess the incident against financial-sector oversight expectations, customer notification duties, and vendor risk obligations.
Mid-sized manufacturer: A manufacturer relies on Exchange to distribute purchase orders, shipping instructions, and supplier invoices. A compromised mail server could interrupt communication with suppliers and create opportunities for invoice fraud through altered or impersonated email activity. Production schedules and customer deliveries could be affected even if factory systems themselves are untouched.
Canadian healthcare provider: A healthcare organization operates Exchange for clinical administration and staff coordination. Exposure of emails containing personal health information could require a privacy assessment and potentially notifications under applicable Canadian privacy requirements. Loss of email availability could also impair scheduling, referrals, and incident coordination.
Professional services firm: A law, accounting, or consulting firm may hold client documents, deal discussions, and privileged correspondence in mailboxes. An Exchange compromise could create confidentiality, contractual, and reputational consequences that extend well beyond the affected server. Rapid containment and credible evidence of patching and monitoring would be vital in communications with clients and insurers.
S4 — Am I Affected?
- You are potentially affected if you operate Microsoft Exchange Server 2016 Cumulative Update 23 below version 15.01.2507.072.
- You are potentially affected if you operate Microsoft Exchange Server 2019 Cumulative Update 14 below version 15.02.1544.044.
- You are potentially affected if you operate Microsoft Exchange Server 2019 Cumulative Update 15 below version 15.02.1748.049.
- You are potentially affected if you operate Microsoft Exchange Server Subscription Edition RTM below version 15.02.2562.046.
- You should investigate if you have on-premises Exchange servers, hybrid Exchange infrastructure, disaster-recovery Exchange servers, or servers managed by a third party.
- You should prioritize review if any Exchange service is reachable from the internet or if broad groups of users, partners, or service accounts can authenticate to it.
- You are not directly affected by this specific server vulnerability if you use only Microsoft-hosted Exchange Online and have no affected on-premises Exchange Server instance.
Key Takeaways
- CVE-2026-62913 is a high-severity Microsoft Exchange Server vulnerability with a CVSS v3.1 score of 8.8 and remote code execution impact.
- Your risk is greatest when you run an affected on-premises Exchange version and an attacker can obtain even low-level authenticated access.
- A successful compromise can affect sensitive email data, business continuity, customer trust, and compliance decision-making.
- Microsoft has released an official fix, so validating versions and applying the relevant security update should be your first priority.
- You should combine patching with account review, restricted external exposure, centralized monitoring, and incident-response readiness.
Call to Action
A patch is essential, but it does not answer every question about exposure, weak credentials, excessive access, or adjacent attack paths. IntegSec helps organizations identify and reduce the risks that attackers use to turn isolated vulnerabilities into business-impacting incidents. Contact IntegSec to schedule a penetration test that evaluates your Exchange exposure, authentication controls, network segmentation, detection capability, and remediation priorities. Build evidence-based confidence in your defenses before an attacker tests them for you.
TECHNICAL APPENDIX
A — Technical Analysis
CVE-2026-62913 is a heap-based buffer overflow in Microsoft Exchange Server, classified as CWE-122. Microsoft states that an authenticated attacker can send a specially crafted request to an affected Exchange service over the network and, if successful, execute code on the target system. The disclosed root cause is therefore unsafe handling of network-supplied data within an affected Exchange service, resulting in memory corruption. The advisory does not publicly identify a more granular Exchange component or endpoint.
Microsoft assigns CVSS v3.1 vector CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H, with a base score of 8.8. The attack vector is network-based, attack complexity is low, low privileges are required, and user interaction is not required. Scope is unchanged, while confidentiality, integrity, and availability impacts are all high. The National Vulnerability Database records Microsoft as the CNA and references the Microsoft Security Response Center advisory; NVD has not supplied an independent score.
B — Detection & Verification
Version enumeration: Run the following in the Exchange Management Shell to obtain installed build information:
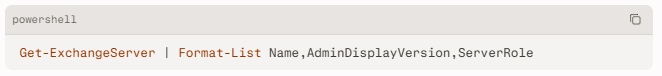
Compare results against fixed builds: Exchange 2016 CU23 15.01.2507.072, Exchange 2019 CU14 15.02.1544.044, Exchange 2019 CU15 15.02.1748.049, and Exchange Server Subscription Edition RTM 15.02.2562.046.
Scanner validation: Use an authenticated vulnerability scan that maps Exchange product and build details to CVE-2026-62913. A useful signature should identify the affected product branch and flag versions below Microsoft’s fixed build, rather than relying only on open ports or service banners.
Log review: Investigators should correlate unusual authenticated requests to Exchange-facing services with application errors, Windows Error Reporting events, process crashes, unexpected service restarts, or memory-corruption symptoms. Review Exchange, IIS, Windows Security, endpoint detection, and authentication logs for unusual activity involving low-privilege accounts.
Network indicators: Investigate anomalous authenticated traffic to Exchange from unusual source addresses, repeated malformed or oversized requests, unexpected outbound connections from the Exchange server, and newly created remote sessions or administrative activity following Exchange service instability. The vendor advisory confirms network delivery through specially crafted requests but does not publish request-level indicators of compromise.
C — Mitigation & Remediation
- Immediate (0–24h): Inventory every on-premises Exchange Server, including hybrid, recovery, and dormant instances. Compare installed builds with Microsoft’s affected and fixed versions, then apply Microsoft’s official security update to affected systems through your approved emergency change process. Confirm successful installation, reboot requirements, service health, mail flow, and the final installed build.
- Immediate (0–24h): Review privileged, service, and user accounts that can authenticate to Exchange. Disable stale accounts, rotate credentials where compromise is suspected, enforce multifactor authentication where supported, and limit external access to Exchange administration and web services through trusted networks or secure access controls. Because exploitation requires low privileges, access hygiene directly reduces opportunity.
- Short-term (1–7d): Run authenticated vulnerability scans and independently verify patch status with Exchange Management Shell. Hunt for unexpected processes, scheduled tasks, new services, suspicious mailbox access, anomalous outbound connections, and authentication anomalies beginning before the patch window. Preserve relevant logs and system evidence if indicators suggest compromise.
- Short-term (1–7d): If immediate patching is impossible, reduce exposure while scheduling a tested maintenance window. Restrict Exchange service access to required networks, remove unnecessary internet exposure, allow only approved reverse-proxy or virtual private network paths, and tighten account access. These measures are compensating controls, not substitutes for Microsoft’s fix.
- Long-term (ongoing): Establish a documented Exchange patch lifecycle, maintain accurate asset and version inventories, test updates in a representative environment, and verify deployment with authenticated scanning. Include Exchange in tabletop exercises and penetration tests that assess credential misuse, internal segmentation, lateral movement, and monitoring effectiveness.
D — Best Practices
- Maintain a complete inventory of Exchange servers, installed cumulative updates, security updates, exposed services, and accountable system owners.
- Apply Microsoft security updates promptly through a risk-based emergency patch process when remote code execution flaws affect email infrastructure.
- Require strong authentication, multifactor authentication where available, and least-privilege permissions for Exchange users, administrators, service accounts, and third parties.
- Restrict Exchange administrative interfaces and externally accessible services to only the networks and identities that require access.
- Centralize Exchange, IIS, Windows, identity, endpoint, and network logs so authenticated abuse and post-exploitation behavior can be correlated quickly
Leave Comment