
CVE-2026-62911: Microsoft Exchange Server Authentication Bypass Bug - What It Means for Your Business and How to Respond
Introduction
CVE-2026-62911 is a high-severity vulnerability in on-premises Microsoft Exchange Server, the email and collaboration platform many organizations still operate within their own environments. For businesses across the United States and Canada, Exchange remains a high-value system because it processes executive communications, customer records, financial discussions, contracts, and credentials-reset workflows.
This issue can let an attacker with limited access abuse weaknesses in the way Exchange handles authentication and authorization, potentially gaining far greater control than their original account should permit. The practical risk is not limited to mailbox access. A successful compromise can disrupt email operations, expose sensitive information, and create a launch point for broader intrusion activity.
This article explains what is known about CVE-2026-62911, the business risks it creates, how to determine whether you may be affected, and the actions your organization should prioritize.
Background & History
Microsoft disclosed CVE-2026-62911 on August 11, 2026, as a Microsoft Exchange Server Elevation of Privilege Vulnerability. Microsoft is the CVE Numbering Authority for the record. The issue affects specified builds of Exchange Server 2016, Exchange Server 2019, and Exchange Server Subscription Edition running on x64 systems. Microsoft assigned a Common Vulnerability Scoring System, or CVSS, score of 8.0 out of 10, rated High.
In plain language, the flaw involves an authentication bypass through capture and replay. An attacker can reuse certain authentication material or requests in a way that Exchange should reject, then obtain privileges beyond those originally granted. The Zero Day Initiative credited Orange Tsai of DEVCORE Research Team and reported that the issue was disclosed to Microsoft on May 21, 2026, followed by coordinated public release on August 11. Microsoft released security updates to correct the vulnerability.
What This Means for Your Business
If you operate an affected, unpatched Exchange Server, CVE-2026-62911 should be treated as a priority because email infrastructure connects directly to business operations. Email is often the channel through which you approve payments, exchange customer information, coordinate legal and human-resources work, distribute invoices, and reset access to other systems.
The vulnerability requires an attacker to have limited privileges and user interaction according to Microsoft’s severity vector. That does not make it low risk. Limited access can arise from a compromised employee account, a malicious insider, exposed credentials, or access obtained through another weakness. Once an attacker expands privileges, the consequences can extend beyond a single mailbox or employee.
For your organization, the potential impact includes unauthorized access to sensitive communications, altered email rules, disruption to internal coordination, and a foothold for further attacks. A compromise can also drive incident-response costs, business interruption, notification obligations, contractual issues, and reputational harm. Canadian organizations should also consider privacy responsibilities under applicable federal and provincial requirements, while U.S. organizations may face sector-specific, state, contractual, and customer-notification obligations.
The immediate business question is straightforward: do you still run on-premises Exchange, and are your servers at Microsoft’s fixed build levels? If the answer is uncertain, treat the environment as needing validation rather than assuming it is safe.
Real-World Examples
Regional bank: A regional bank uses Exchange Server for internal lending discussions, wire-transfer approvals, and customer-service communications. An attacker who first obtains a low-privilege employee account could exploit a vulnerable Exchange server to gain greater access, review sensitive correspondence, and attempt fraud through manipulated approval workflows. The incident could trigger customer notifications, regulatory scrutiny, and operational disruption during containment.
Mid-sized manufacturer: A manufacturer relies on email to coordinate suppliers, shipping schedules, production changes, and invoices across the United States and Canada. Compromise of Exchange could expose vendor communications and permit attackers to impersonate trusted staff, increasing the risk of payment-diversion fraud or supply-chain disruption. Even a short period of email unavailability can delay orders and affect customer commitments.
Healthcare provider group: A multi-clinic healthcare organization hosts Exchange on premises to support scheduling, referrals, billing coordination, and administrative communication. A successful privilege escalation could place protected or personal information at risk and require a formal investigation into the scope of exposure. The resulting downtime may also impair patient-facing operations and place additional pressure on already limited IT resources.
Canadian professional-services firm: A law, accounting, or consulting firm may use Exchange for confidential client files, merger discussions, tax records, and identity documents. Elevated access could allow an attacker to search mailboxes, obtain sensitive attachments, or establish persistence for later espionage or extortion. The business impact would center on client trust, confidentiality commitments, and potential privacy reporting decisions.
Am I Affected?
- You are potentially affected if you operate on-premises Microsoft Exchange Server, rather than relying exclusively on Microsoft-hosted Exchange Online.
- You are affected if Exchange Server 2016 Cumulative Update 23 is running a build earlier than 15.01.2507.072.
- You are affected if Exchange Server 2019 Cumulative Update 14 is running a build earlier than 15.02.1544.044.
- You are affected if Exchange Server 2019 Cumulative Update 15 is running a build earlier than 15.02.1748.049.
- You are affected if Exchange Server Subscription Edition RTM is running a build earlier than 15.02.2562.046.
- You should investigate immediately if your inventory is incomplete, patching is decentralized, or external IT providers manage Exchange without giving you verified patch-status reports.
- You should confirm that disaster-recovery, staging, and geographically distributed Exchange servers are included, not only the primary production server.
Key Takeaways
- CVE-2026-62911 is a high-severity Microsoft Exchange Server vulnerability that can enable authentication bypass by capture and replay and subsequent privilege escalation over a network.
- Your organization faces greater risk when an affected Exchange server remains unpatched and an attacker can first obtain limited access through compromised credentials or another intrusion path.
- Exchange servers require priority because they handle business-critical communications, sensitive information, identity workflows, and operational coordination.
- Microsoft has released updates for affected Exchange Server 2016, Exchange Server 2019, and Exchange Server Subscription Edition builds, so you should verify versions against the vendor-provided fixed builds.
- Patching is necessary, but you should also investigate for signs of unauthorized access and validate that email infrastructure is appropriately segmented, monitored, and tested.
Call to Action
A patch closes a known vulnerability, but it does not prove that your Exchange environment has not already been exposed or that adjacent attack paths are secure. IntegSec helps organizations identify exploitable weaknesses across external infrastructure, internal networks, identity systems, and critical business applications. Engage IntegSec for a focused penetration test and practical cybersecurity risk-reduction plan that helps you validate remediation, prioritize real business risk, and strengthen your defenses with confidence.
Technical Appendix
A — Technical Analysis
CVE-2026-62911 is classified as CWE-294, Authentication Bypass by Capture-replay. Microsoft describes the issue as an authentication bypass by capture and replay in Exchange Server that allows an authorized attacker to elevate privileges over a network. The affected products are Exchange Server 2016 CU23, Exchange Server 2019 CU14 and CU15, and Exchange Server Subscription Edition RTM below their respective fixed build numbers.
The Microsoft CVSS 3.1 base vector is CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:H/I:H/A:H, producing a score of 8.0 High. This indicates network reachability, low attack complexity, low privileges required, user interaction required, unchanged scope, and high confidentiality, integrity, and availability impact.
ZDI characterizes the affected area as Exchange authorization-request handling and identifies improper session management as the root cause. Its advisory states that an attacker may combine the flaw with other vulnerabilities to execute code as SYSTEM. ZDI assigned 8.8 using a vector that differs from Microsoft’s published CVSS assessment, including no user interaction. Defenders should use Microsoft’s official guidance and fixed build numbers for remediation decisions.
B — Detection & Verification
Version enumeration: On an Exchange Management Shell host, administrators can enumerate installed Exchange build details with:
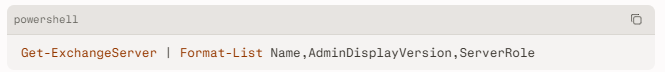
Administrators should compare AdminDisplayVersion values to Microsoft’s fixed versions: 15.01.2507.072 for Exchange 2016 CU23, 15.02.1544.044 for Exchange 2019 CU14, 15.02.1748.049 for Exchange 2019 CU15, and 15.02.2562.046 for Subscription Edition RTM.
Scanner coverage: Vulnerability scanners should identify Exchange product edition, cumulative update, and exact installed build, then flag builds below the vendor’s remediation thresholds. Confirm authenticated-scan credentials can read current patch state and include all Exchange servers, such as disaster-recovery and hybrid infrastructure.
Log review: Security teams should investigate unusual authentication and authorization events, unexpected mailbox-access patterns, unfamiliar Outlook Web App or Exchange Control Panel activity, and new or modified mailbox rules. They should also review administrator and service-account activity that does not match established operating patterns.
Behavioral indicators: Escalating privileges, changes to Exchange configuration, unexpected account creation, suspicious remote administration, and anomalous outbound authentication traffic warrant investigation. These are behavioral leads, not CVE-specific indicators of compromise.
C — Mitigation & Remediation
- Immediate (0–24h): Identify every on-premises Exchange server, including production, disaster-recovery, test, hybrid, and isolated administrative environments. Compare each installed version with Microsoft’s affected ranges and fixed build numbers. Apply Microsoft’s official security update first wherever normal change-control procedures permit. Record the installed version and successful update status for every server.
- Immediate (0–24h): If a server cannot be patched immediately, reduce its exposure while maintaining business continuity. Restrict Exchange administrative interfaces and remote access to approved management networks, require multifactor authentication for administrative access, remove unnecessary internet exposure, and limit access through firewall rules or secure access gateways. These controls reduce opportunity but do not remediate the underlying flaw.
- Short-term (1–7d): Validate that patched servers report a fixed build version and restart required services or servers according to Microsoft’s update guidance. Review Exchange authentication, administrator, mailbox-rule, and configuration-change activity for anomalous behavior before and after patching. Reset credentials and revoke active sessions if investigation identifies suspicious access.
- Short-term (1–7d): Conduct an authenticated vulnerability scan and a targeted review of Exchange attack surface, identity dependencies, remote-management paths, and backup systems. Confirm that no older Exchange instances remain in branch offices, labs, recovery sites, or decommissioning queues.
- Long-term (ongoing): Establish a disciplined Exchange patch-management program with accountable owners, asset inventory, patch-service targets, maintenance windows, rollback procedures, and post-patch validation. Segment email infrastructure, minimize privileged accounts, monitor high-value identity events, and periodically test whether an attacker can move from a low-privilege foothold to administrative control.
D — Best Practices
- Maintain a continuously verified inventory of Exchange servers, installed cumulative updates, and exact build versions so that security teams can quickly determine exposure to vendor advisories.
- Apply Microsoft security updates promptly after risk-based testing, with explicit escalation procedures for internet-facing or business-critical email infrastructure.
- Limit administrator access to Exchange servers through separate privileged accounts, multifactor authentication, approved management workstations, and network access restrictions.
- Monitor authorization changes, account privilege changes, mailbox delegation, mailbox-rule creation, and Exchange configuration modifications for unauthorized activity.
- Test identity and email infrastructure through regular penetration testing to identify whether low-privilege access can be expanded into high-value administrative control.
Leave Comment