
CVE-2026-62827: Microsoft SharePoint Server Improper Authentication Bug - What It Means for Your Business and How to Respond
Introduction
CVE-2026-62827 is a high-severity security vulnerability affecting on-premises Microsoft SharePoint Server deployments. If your organization uses SharePoint to store documents, manage collaboration sites, support intranets, or share sensitive information with employees, customers, suppliers, or partners, this issue deserves prompt attention.
The vulnerability could allow an authenticated user to obtain permissions beyond those they were intended to have. In business terms, a user who should have limited access may be able to reach confidential files, alter important content, or disrupt collaboration systems if the vulnerability is successfully exploited.
This is especially relevant for organizations in the United States and Canada that rely on SharePoint for regulated data, intellectual property, human resources materials, financial records, legal files, or operational documentation. This post explains the vulnerability’s history, its practical business implications, how to determine whether you are affected, and the recommended response. A technical appendix follows for security, infrastructure, and penetration testing teams.
S1 — Background & History
Microsoft published CVE-2026-62827 on August 11, 2026. The issue affects Microsoft SharePoint Enterprise Server 2016, SharePoint Server 2019, and SharePoint Server Subscription Edition when they are running vulnerable builds. Microsoft is the reporting and assigning authority for this vulnerability, and the National Vulnerability Database lists Microsoft as the source.
The vulnerability received a Common Vulnerability Scoring System score of 8.8 out of 10, rated High severity. It is categorized as improper authentication, meaning the affected system may not adequately validate whether a user is entitled to perform a requested action. An attacker must already have some level of authorized access, but does not need to trick another user into clicking a link or opening a file.
The public record was published on August 11 and updated by the National Vulnerability Database on August 12, 2026. Microsoft’s advisory is referenced by the National Vulnerability Database as both the vendor advisory and the source of the security patch.
S2 — What This Means for Your Business
For your business, CVE-2026-62827 is primarily an access-control and trust problem. SharePoint often functions as a central location for shared work, including board materials, engineering plans, customer contracts, finance reports, merger discussions, employee records, and internal policies. If a legitimate but insufficiently privileged account can gain elevated permissions, your security boundaries inside SharePoint may no longer operate as intended.
Operationally, unauthorized changes to documents, permissions, lists, or sites can slow teams down and create uncertainty about which information is accurate. A compromised employee, contractor, service account, or partner account could potentially access content outside its approved role. That creates a risk of business interruption even when core systems remain online.
The data risk can be substantial. Exposure of personally identifiable information, protected health information, payment-related documents, trade secrets, or confidential client data may trigger notification, contractual, insurance, and regulatory obligations. Organizations subject to U.S. state privacy requirements, Canadian privacy obligations, industry rules, or customer security commitments should assess whether SharePoint repositories hold sensitive information.
Reputational damage also matters. Customers and partners expect you to limit access based on job function and enforce separation between sensitive business areas. A privilege escalation incident can undermine that confidence, particularly if it affects shared portals or documents containing third-party information. The appropriate response is disciplined patching, access review, log analysis, and independent validation of SharePoint security controls.
S3 — Real-World Examples
Regional bank: A regional bank uses on-premises SharePoint for loan underwriting packages, internal audit evidence, and policy documentation. A user with ordinary access could potentially obtain elevated access and view information that should be restricted to lending leadership, compliance personnel, or internal audit teams.
The immediate impact may include a sensitive-data investigation, access reviews, and potential obligations under financial-sector policies and customer commitments. The business also faces uncertainty over whether confidential records were viewed or copied.
Canadian healthcare provider: A healthcare provider uses SharePoint to coordinate internal procedures, vendor documents, workforce schedules, and administrative files containing personal information. A compromised or misused staff account could gain permissions beyond its approved responsibilities.
Even if clinical systems are not directly affected, you could face disruption while teams investigate SharePoint access, preserve logs, reset credentials, and validate file permissions. The event may also require privacy review because administrative repositories can still contain sensitive patient or employee information.
Mid-market manufacturer: A manufacturer stores product designs, supplier pricing, quality records, and merger-related materials in SharePoint. An attacker who first obtains a low-privilege account could seek higher access to collect intellectual property or manipulate documents used in production and procurement workflows.
The resulting harm could include loss of negotiating leverage, exposure of proprietary designs, delayed operations, and difficult questions from suppliers or customers. Your response should focus on both patching and determining whether abnormal access occurred before the update.
Professional services firm: A legal, accounting, or consulting firm may use SharePoint workspaces to collaborate on client engagements. Elevated access could expose files from unrelated clients, creating confidentiality and contractual concerns even when the attacker has valid credentials for a different matter.
Your firm may need to assess document access history, preserve evidence, notify affected clients when warranted, and demonstrate that stronger access controls have been implemented.
S4 — Am I Affected?
- You are potentially affected if you operate Microsoft SharePoint Enterprise Server 2016 with a build earlier than 16.0.5565.1001.
- You are potentially affected if you operate Microsoft SharePoint Server 2019 with a build earlier than 16.0.10417.20198.
- You are potentially affected if you operate SharePoint Server Subscription Edition with a build earlier than 16.0.19725.20522.
- You should prioritize review if your SharePoint environment is reachable by contractors, partners, remote employees, or other users outside a tightly controlled internal network.
- You should treat the issue as business-critical if SharePoint contains regulated, confidential, customer, employee, financial, legal, or intellectual-property data.
- You are less likely to be directly affected if you use Microsoft 365 SharePoint Online only, rather than the listed on-premises SharePoint Server products; confirm your deployment model with your Microsoft administrator before closing the issue.
- You should investigate immediately if you find unexpected changes to permissions, group membership, site ownership, document access patterns, or administrative activity.
Key Takeaways
- CVE-2026-62827 is a High-severity Microsoft SharePoint Server vulnerability with a CVSS score of 8.8 that can enable an authorized network user to elevate privileges.
- The issue affects specific vulnerable builds of SharePoint Server 2016, SharePoint Server 2019, and SharePoint Server Subscription Edition.
- Your highest business risks are unauthorized access to sensitive information, improper document changes, operational disruption, and compliance or contractual exposure.
- Apply Microsoft’s security update promptly, then verify that the update succeeded across every SharePoint server and farm component.
- Treat patching as the beginning of the response, not the end: review permissions, investigate suspicious activity, and validate your SharePoint access controls through security testing.
Call to Action
Your SharePoint environment may hold some of your organization’s most sensitive operational and customer information. IntegSec helps organizations identify exploitable weaknesses, validate access boundaries, and reduce cybersecurity risk before a vulnerability becomes a business incident.
Engage IntegSec for a focused SharePoint assessment or a broader penetration test that evaluates authentication, authorization, privilege boundaries, exposed services, and practical attack paths across your environment. Get a clear, prioritized view of what needs attention and how to address it. Visit IntegSec to start the conversation.
TECHNICAL APPENDIX
A — Technical Analysis
CVE-2026-62827 is an improper authentication vulnerability in Microsoft Office SharePoint Server. The documented impact is elevation of privilege over a network by an attacker who is already authorized to access the affected SharePoint instance. The flaw is mapped to CWE-287, Improper Authentication.
Microsoft assigned a CVSS v3.1 base score of 8.8, High, with vector CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:H. This indicates network reachability, low attack complexity, required low privileges, no user interaction, unchanged scope, and high impact to confidentiality, integrity, and availability. The available public description does not disclose a detailed vulnerable code path or endpoint, so defenders should not assume a particular SharePoint feature, web part, workflow, or application page is unaffected without applying the vendor update.
The National Vulnerability Database identifies the affected product families as SharePoint Enterprise Server 2016, SharePoint Server 2019, and SharePoint Server Subscription Edition below the stated fixed builds.
B — Detection & Verification
Version enumeration: Administrators can use SharePoint Management Shell to identify farm and server builds:
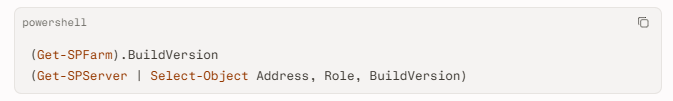
Compare results with the fixed versions: 16.0.5565.1001 for SharePoint Enterprise Server 2016, 16.0.10417.20198 for SharePoint Server 2019, and 16.0.19725.20522 for SharePoint Server Subscription Edition.
Scanner identification: Vulnerability scanners should identify product version and installed SharePoint security update state, then flag systems below the applicable fixed build. Detection should be authenticated where possible because externally visible version information may be incomplete or suppressed.
Log review: Investigators should review SharePoint Unified Logging System records, Internet Information Services logs, Windows Security Event Logs, Active Directory change events, and SharePoint audit records for unexpected permission elevation, role changes, site collection administration changes, or unusual document access.
Behavioral anomalies: Look for low-privilege accounts accessing administrative sites, restricted libraries, executive workspaces, human resources repositories, or unrelated customer data. Also investigate unusual account activity that occurs outside normal location, time, or application-use patterns.
Network indicators: There is no public exploit signature identified in the official records reviewed. Defenders should therefore prioritize anomaly-based detection, authenticated configuration assessment, and correlation of web requests with authorization changes rather than relying solely on a fixed network signature.
C — Mitigation & Remediation
- Immediate (0–24h): Inventory every on-premises SharePoint Server 2016, 2019, and Subscription Edition deployment, including disaster-recovery systems, development farms, and isolated business-unit instances. Identify each farm’s installed build and prioritize externally accessible systems, systems containing sensitive data, and systems with large populations of contractors or partner users. Apply the Microsoft security update associated with CVE-2026-62827 and confirm the resulting build meets or exceeds the applicable fixed version.
- Immediate (0–24h): Preserve relevant SharePoint, Internet Information Services, Windows, identity-provider, and security-information-and-event-management logs before retention periods expire. Review recent changes to site owners, SharePoint groups, permissions, service accounts, and high-value document repositories. Reset or revoke sessions for suspicious accounts and remove unexpected privileged assignments.
- Short-term (1–7d): Conduct an entitlement review for SharePoint farm administrators, site collection administrators, application pool identities, service accounts, and privileged SharePoint groups. Ensure privileged accounts are separate from standard user accounts, protected by multifactor authentication where supported, and not used for routine browsing or document collaboration.
- Short-term (1–7d): If you cannot patch immediately, reduce exposure by limiting SharePoint network access to approved corporate networks and managed virtual private network access, restricting contractor and partner access, removing unnecessary internet publishing, and applying strict web application firewall monitoring. These measures reduce opportunity but do not remediate the vulnerability.
- Long-term (ongoing): Establish a SharePoint-specific vulnerability management process that includes asset ownership, patch validation, configuration baselines, periodic permissions recertification, centralized logging, and authenticated vulnerability scans. Validate remediation with an independent penetration test that examines privilege escalation paths and access-control enforcement.
D — Best Practices
- Maintain an authoritative inventory of every SharePoint farm, server role, build version, owner, data classification, and internet exposure status.
- Apply SharePoint security updates through a controlled but urgent patch-management process, including backup, change control, installation verification, and post-update service validation.
- Enforce least privilege by limiting farm administrator, site collection administrator, site owner, and document-library permission assignments to documented business need.
- Separate privileged SharePoint administration accounts from normal employee accounts and monitor them for unusual sign-in, permission, and content-access activity.
- Collect and retain SharePoint, web server, Windows, directory, and identity logs long enough to support incident investigation and access-history review
Leave Comment