
CVE-2026-62823: Windows DHCP Server Remote Code Execution Bug - What It Means for Your Business and How to Respond
Introduction
CVE-2026-62823 is a high-severity security vulnerability in Microsoft Windows DHCP Server, a service many organizations rely on to automatically assign network settings to employee devices, servers, phones, printers, and other connected equipment. If your organization operates affected Windows Server systems as DHCP servers, this issue deserves prompt attention because a successful attack could give an unauthorized person control over a critical network infrastructure system.
The risk is most relevant to organizations with on-premises networks, branch offices, hybrid environments, warehouses, healthcare facilities, schools, and other locations where Windows-based DHCP services support day-to-day connectivity. For businesses across the United States and Canada, the impact can extend beyond one server: disruption to DHCP can affect users’ ability to connect, while server compromise can create a path to broader network intrusion.
This post explains the business implications, practical exposure checks, and response priorities. A technical appendix follows for security engineers, IT administrators, and penetration testers.
S1 — Background & History
Microsoft published CVE-2026-62823 on August 11, 2026, identifying a remote code execution vulnerability in Windows DHCP Server. Microsoft is the reporting organization and Common Vulnerabilities and Exposures numbering authority for the record. The vulnerability received a Common Vulnerability Scoring System version 3.1 score of 8.8 out of 10, classified as High severity.
In plain language, the flaw can occur when the affected service handles certain network data incorrectly. An unauthorized attacker on an adjacent network can potentially trigger a memory-handling error and run code on the DHCP server. The attacker does not need prior sign-in credentials or user interaction, but must be able to reach the relevant network environment.
The vulnerability was disclosed as part of Microsoft’s August 2026 security updates. The National Vulnerability Database lists affected Windows Server 2012, 2012 R2, 2016, 2019, 2022, and 2025 releases, including several Server Core deployments, when below the specified patched versions.
S2 — What This Means for Your Business
For your business, CVE-2026-62823 is not merely a software maintenance item. DHCP is foundational network infrastructure. It provides devices with the configuration they need to communicate on your network. If an attacker compromises a DHCP server, the immediate concern is the server itself, but the practical business exposure can expand to systems and services that depend on reliable internal connectivity.
An attacker who gains code execution could potentially interrupt network services, alter configurations, deploy malicious software, or use the compromised system as a staging point for broader movement through your environment. That can delay operations in offices, retail locations, plants, logistics sites, or distributed branches. It can also increase recovery costs, divert internal technology staff, and create downtime for employees and customer-facing services.
There are also data and governance implications. A compromised infrastructure server may provide access to configuration data, administrator activity, or connected systems. For organizations subject to privacy, contractual, financial-services, healthcare, or public-sector requirements in the United States or Canada, an incident may trigger investigation, documentation, notification, and audit obligations.
The key business question is straightforward: identify whether you run an affected Windows DHCP Server, apply Microsoft’s security update through your established change process, and verify that network controls limit unnecessary access to the service.
S3 — Real-World Examples
A regional bank: A regional bank uses Windows DHCP Server across branches to connect workstations, teller devices, and internal administrative systems. If an attacker on a reachable network segment compromises the DHCP server, the bank could face branch connectivity disruption and an expanded investigation into whether the attacker accessed systems supporting customer operations. The business impact may include service delays, incident-response costs, and scrutiny from regulators and customers.
A Canadian manufacturing company: A manufacturer operates Windows DHCP services for office networks, warehouse scanners, engineering workstations, and operational support devices. A compromise could interrupt network access for equipment that depends on automatic configuration, delaying shipping, inventory updates, or production coordination. Even if production systems are separately segmented, recovery resources may be pulled away from normal operations.
A midsize healthcare provider: A healthcare organization uses DHCP services in clinics and administrative offices. If a vulnerable server is exploited, staff may experience connectivity failures involving workstations, printers, and internal applications, affecting patient intake and care coordination. The organization would also need to evaluate whether protected information or systems containing it were exposed during the incident.
A multi-location professional-services firm: A firm with offices in several U.S. and Canadian cities centrally manages Windows servers but has inconsistent patching at smaller sites. One overlooked DHCP server could become an entry point from a local network, leading to expensive forensic work and a loss of client confidence if the incident affects confidential matter data. The risk is higher when infrastructure servers are not segmented from everyday user networks.
S4 — Am I Affected?
- You are likely affected if you operate Microsoft Windows Server as a Dynamic Host Configuration Protocol, or DHCP, server and have not applied Microsoft’s August 2026 security update for this vulnerability.
- You are affected if you run Windows Server 2012 or Server Core below build 6.2.9200.26280, or Windows Server 2012 R2 or Server Core below build 6.3.9600.23338.
- You are affected if you run Windows Server 2016 below build 10.0.14393.9418 or Windows Server 2019 below build 10.0.17763.9121.
- You are affected if you run Windows Server 2022 below build 10.0.20348.5499 or Windows Server 2025, including Server Core, below build 10.0.26100.33296.
- You may not be affected if Windows DHCP Server is not installed or enabled in your environment, but you should validate this through asset inventory and configuration review rather than assumption.
- You should treat exposure as higher when untrusted, guest, bring-your-own-device, partner, or poorly segmented networks can reach your DHCP infrastructure.
Key Takeaways
- CVE-2026-62823 is a High-severity Windows DHCP Server vulnerability with a CVSS 3.1 score of 8.8 and potential for unauthorized code execution from an adjacent network.
- Your priority is to identify all Windows systems performing DHCP functions, including systems at branch offices and Server Core installations.
- A successful compromise can affect network availability, increase the chance of wider intrusion, and create costly response, compliance, and reputation consequences.
- Microsoft’s security update is the primary remediation, and patch status should be confirmed against the affected version thresholds.
- Network segmentation and restricted access to DHCP infrastructure reduce exposure while patching and strengthen resilience after remediation.
Call to Action
CVE-2026-62823 is a useful reminder that core infrastructure deserves the same disciplined security attention as internet-facing applications. IntegSec can help you validate exposure, test network segmentation, assess lateral-movement paths, and prioritize practical remediation through an expert penetration test. Strengthen the security controls that protect your business operations before a vulnerability becomes an incident. Contact IntegSec to discuss a focused cybersecurity risk-reduction assessment.
Technical Appendix
A — Technical Analysis
CVE-2026-62823 is a heap-based buffer overflow, classified as CWE-122, in the Microsoft Windows DHCP Server service. The published description states that an unauthorized attacker can execute code over an adjacent network by triggering the condition in the service’s processing of DHCP-related network traffic.
Microsoft assigned a CVSS 3.1 base score of 8.8, with vector CVSS:3.1/AV:A/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H. This indicates an adjacent-network attack vector, low attack complexity, no privileges required, no user interaction, unchanged scope, and high potential impact to confidentiality, integrity, and availability.
The affected component is Windows DHCP Server, including listed Windows Server and Server Core releases. The Common Vulnerabilities and Exposures record identifies Microsoft as the reporting authority and links to the Microsoft Security Response Center advisory, while the National Vulnerability Database provides affected-product and weakness information. Exploitation requires network proximity or reachability rather than general internet exposure, so subnet boundaries, relay configurations, virtual network design, and wireless or guest-network isolation materially affect real-world exposure.
B — Detection & Verification
Version enumeration: Administrators can use the following PowerShell commands to identify the operating system build and determine whether DHCP Server is installed:
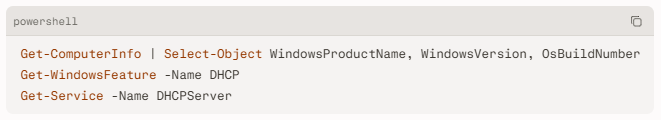
Compare the resulting build with Microsoft’s published fixed-version thresholds. Windows Server 2012, 2012 R2, 2016, 2019, 2022, and 2025 are affected below their respective remediated builds.
Scanner coverage: Vulnerability scanners should identify CVE-2026-62823 through authenticated operating-system version checks and, where available, DHCP Server role detection. A network intrusion-prevention signature is also available from Trend Micro as rule 1012634 for this vulnerability.
Log indicators: Investigators should review Windows System and DHCP Server logs for unexpected service termination, restart events, abnormal faulting behavior, or repeated DHCP processing errors near suspicious network activity. Correlate those events with endpoint telemetry for new processes, unusual administrator activity, persistence mechanisms, or security-control tampering on DHCP servers.
Network indicators: Defenders should investigate anomalous DHCP traffic patterns, malformed or unexpectedly large DHCP packets, unusual traffic reaching DHCP servers from untrusted segments, and DHCP activity originating outside authorized network paths.
C — Mitigation & Remediation
- Immediate (0–24h): Identify every Windows system with the DHCP Server role installed and running. Compare installed operating-system builds against Microsoft’s affected-version guidance, then prioritize servers that service corporate, branch, wireless, operational, or mixed-trust networks. Apply Microsoft’s official security update first through approved emergency-change procedures and reboot systems where required.
- Immediate (0–24h): Until patching is complete, restrict DHCP-related traffic so only intended network segments, approved DHCP relay agents, and authorized infrastructure devices can reach DHCP servers. Isolate guest, contractor, wireless, lab, and bring-your-own-device networks from production DHCP infrastructure. These controls are interim risk reduction, not substitutes for the vendor update.
- Short-term (1–7d): Validate successful remediation using authenticated vulnerability scans, operating-system build checks, and DHCP role inventories. Confirm that failover partners, standby servers, branch appliances, Server Core systems, and disaster-recovery instances are included. Review endpoint detection and response telemetry plus DHCP and System logs for evidence of service instability or suspicious processes before and after remediation.
- Short-term (1–7d): Conduct a focused network-segmentation review. Verify that user networks, guest networks, management networks, and high-value server segments enforce intended boundaries. Remove unnecessary DHCP service exposure and ensure rogue DHCP detection and monitoring are enabled where supported.
- Long-term (ongoing): Establish recurring infrastructure vulnerability management that combines accurate asset inventory, timely Microsoft update deployment, authenticated verification, exception tracking, and penetration testing. Include DHCP servers in recovery exercises because a failure or compromise of network-addressing services can affect many dependent systems simultaneously.
D — Best Practices
- Maintain an authoritative inventory of every device running Windows DHCP Server, including Server Core, branch-office, failover, standby, and disaster-recovery instances.
- Apply Microsoft security updates according to risk-based service-level targets, with an expedited process for high-severity vulnerabilities affecting infrastructure roles.
- Segment DHCP infrastructure from user, guest, wireless, contractor, and operational networks to limit adjacent-network access.
- Allow DHCP communications only through approved network paths, relay agents, and firewall rules, and review those rules after network changes.
- Monitor DHCP Server health, Windows event logs, endpoint telemetry, and abnormal DHCP traffic for signs of malformed requests, crashes, unauthorized code execution, or rogue service activity
Leave Comment