
CVE-2026-54725: vault-secrets-webhook SSRF Vulnerability - What It Means for Your Business and How to Respond
Introduction
If your organization runs Kubernetes workloads that rely on HashiCorp Vault for secret management, CVE-2026-54725 demands your immediate attention. This critical-severity vulnerability affects vault-secrets-webhook, a widely deployed component that injects secrets directly into Kubernetes pods. Attackers can exploit this flaw to redirect sensitive authentication tokens to systems they control, potentially compromising your entire cloud infrastructure. This post explains what this vulnerability means for your business operations, how to determine if you are affected, and what steps you should take right now to protect your organization.
Background & History
CVE-2026-54725 was published to the National Vulnerability Database on July 31, 2026, following disclosure by security researchers examining the bank-vaults project. The vulnerability carries a CVSS 3.1 base score of 9.6, classifying it as critical severity. It is a Server-Side Request Forgery (SSRF) vulnerability, categorized under CWE-918, affecting vault-secrets-webhook versions prior to 1.23.1. The flaw exists in how the webhook processes the vault-addr annotation from Kubernetes ConfigMaps and Secrets. When an attacker controls this annotation value, the webhook makes outbound HTTP calls to attacker-specified addresses during the admission review process. This behavior allows theft of ServiceAccount JWT tokens, which grant access to your Kubernetes cluster. The vendor released version 1.23.1 to address this issue on the same day the CVE was published.
What This Means for Your Business
This vulnerability poses serious risks to your business operations, data security, and regulatory compliance posture. If exploited, attackers can steal Kubernetes ServiceAccount tokens, which function as master keys to your cloud infrastructure. With these credentials, they can access sensitive data stored in your containers, modify your applications, or even pivot to other systems in your network. For organizations in regulated industries such as finance, healthcare, or government contracting, this type of breach can trigger mandatory reporting obligations under frameworks like PCI DSS, HIPAA, or CMMC. Your customers and partners expect you to protect their data. A breach stemming from an unpatched critical vulnerability can damage your reputation and erode trust that took years to build. Beyond immediate technical impact, you may face contractual penalties, increased insurance premiums, and costly incident response efforts. The good news is that a patch exists. Taking action now demonstrates due diligence and significantly reduces your exposure to these business risks.
Real-World Examples
Regional Financial Institution: A mid-sized credit union running vault-secrets-webhook version 1.22.2 in its Kubernetes cluster processes member account data through containerized applications. An attacker with write access to ConfigMaps in a watched namespace modifies the vault-addr annotation to point to a malicious server. The webhook sends ServiceAccount tokens to this server during routine secret injection, allowing the attacker to access database credentials and exfiltrate member information. The institution faces regulatory scrutiny and member notification costs.
Healthcare Technology Provider: A digital health platform serving clinics across North America uses vault-secrets-webhook to manage API keys and encryption keys for patient records. The vulnerability allows an insider threat or compromised developer account to redirect token requests to an external server. Patient health information becomes accessible to unauthorized parties, triggering HIPAA breach notification requirements and potential fines from the Office for Civil Rights.
E-Commerce Retailer: An online retailer with seasonal traffic spikes runs its shopping platform on Kubernetes with vault-secrets-webhook version 1.21.3 for secret management. During a promotional period, attackers exploit the SSRF flaw to steal tokens and inject malicious code into the checkout process. Payment card data flows to attacker infrastructure, resulting in PCI DSS non-compliance findings and mandatory forensic investigation costs.
SaaS Startup: A fast-growing software company with limited security staff deploys vault-secrets-webhook 1.22.0 to accelerate development velocity. A misconfigured CI/CD pipeline allows an external contributor to submit a pull request that modifies the vault-addr annotation. The webhook sends cluster tokens to the attacker's server, compromising the entire development environment and exposing customer source code repositories
Am I Affected?
You are affected by CVE-2026-54725 if any of the following conditions apply to your environment:
- You are running vault-secrets-webhook version 1.23.0 or earlier in any Kubernetes cluster.
- Your organization uses the bank-vaults project to inject secrets from HashiCorp Vault into pods.
- Your Kubernetes workloads rely on vault.security.banzaicloud.io/* annotations for Vault integration.
- You have ConfigMaps or Secrets in namespaces watched by the webhook that accept user-supplied annotation values.
- Your cluster grants token creation permissions cluster-wide without strict RBAC controls on annotation modifications.
If you answered yes to any of these items, you should treat your environment as at risk until you confirm patching or implement mitigations.
Key Takeaways
- CVE-2026-54725 is a critical SSRF vulnerability in vault-secrets-webhook that can expose your Kubernetes ServiceAccount tokens to attackers.
- Organizations running versions prior to 1.23.1 should patch immediately to prevent credential theft and potential cluster compromise.
- Business impacts include data breaches, regulatory penalties, reputational damage, and costly incident response efforts.
- You can verify your exposure by checking your vault-secrets-webhook version and auditing annotation permissions in your Kubernetes namespaces.
- IntegSec can help you assess your Kubernetes security posture and reduce risk through targeted penetration testing.
Call to Action
Do not wait for an incident to reveal gaps in your Kubernetes security. Contact IntegSec today to schedule a penetration test focused on your cloud infrastructure and secret management practices. Our team will identify vulnerabilities like CVE-2026-54725 before attackers do and provide actionable recommendations to strengthen your defenses. Visit https://integsec.com to learn how we help organizations across the USA and Canada reduce cybersecurity risk with confidence.
Technical Appendix
A — Technical Analysis
CVE-2026-54725 stems from unsafe handling of the vault.security.banzaicloud.io/vault-addr annotation in vault-secrets-webhook. The parseVaultConfig() function in pkg/webhook/config.go accepts this annotation without validation. When MutateConfigMap or MutateSecret is called, the webhook invokes newVaultClient in pkg/webhook/webhook.go, which makes an outbound HTTP request to the attacker-specified address. The vault.security.banzaicloud.io/vault-serviceaccount annotation further enables theft of ServiceAccount JWT tokens via the TokenRequest API. This SSRF vulnerability has a CVSS 3.1 vector of AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:N, reflecting network exploitability, low attack complexity, low privileges required, no user interaction, scope change, and high impact on confidentiality and integrity. The NVD reference is https://nvd.nist.gov/vuln/detail/CVE-2026-54725, and the associated CWE is CWE-918 (Server-Side Request Forgery).
B — Detection & Verification
Version enumeration commands:
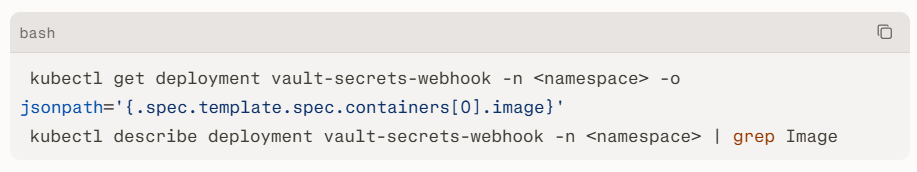
Scanner signatures: Security scanners such as Trivy, Snyk, or Dependabot will flag vault-secrets-webhook images tagged below 1.23.1 as vulnerable to CVE-2026-54725.
Log indicators: Look for outbound HTTP requests from the webhook pod to unexpected external IP addresses or domains, especially during admission review events.linkedin
Behavioral anomalies: Monitor for unusual TokenRequest API calls originating from the webhook service account, particularly requests for ServiceAccount JWTs that do not match expected Vault addresses.
Network exploitation indicators: Egress traffic from Kubernetes nodes to attacker-controlled infrastructure on ports 80 or 443 during ConfigMap or Secret creation/modification events may indicate active exploitation.
C — Mitigation & Remediation
1. Immediate (0–24h): Upgrade vault-secrets-webhook to version 1.23.1 or later. This is the official vendor patch and the only complete remediation. If immediate patching is not feasible, restrict write access to ConfigMaps and Secrets in namespaces watched by the webhook using Kubernetes RBAC. Audit and remove any vault-addr annotations that point to untrusted addresses.
2. Short-term (1–7d): Implement network policies to limit egress traffic from the webhook pod to only known, trusted Vault server addresses. Enable audit logging for the TokenRequest API and monitor for anomalous service account token requests. Review and harden RBAC policies to ensure only authorized principals can modify annotations in webhook-watched namespaces.
3. Long-term (ongoing): Adopt a principle of least privilege for all Kubernetes service accounts and annotations. Integrate vulnerability scanning into your CI/CD pipeline to detect vulnerable container images before deployment. Establish a regular patch management schedule for all Kubernetes add-ons and admission webhooks. Consider implementing admission controllers that validate annotation values against an explicit allowlist before they reach the webhook.
D — Best Practices
- Validate all user-supplied annotation values against an explicit allowlist before using them in network requests or configuration.
- Restrict RBAC permissions to prevent unauthorized modification of ConfigMaps and Secrets in namespaces watched by admission webhooks.
- Implement egress network policies to limit outbound traffic from Kubernetes system components to only trusted destinations.
- Monitor audit logs for TokenRequest API calls and alert on anomalies such as unexpected service account token requests.
- Integrate container image scanning into your deployment pipeline to detect vulnerable versions of Kubernetes add-ons before they reach production.
Leave Comment