
CVE-2026-44513: Hugging Face Diffusers trust_remote_code Bypass — What It Means for Your Business and How to Respond
Introduction
If your organization uses AI or machine learning models—especially those built on Hugging Face’s Diffusers library—CVE-2026-44513 represents a serious operational and security risk. This vulnerability allows attackers to execute arbitrary code on systems that load untrusted model repositories, even when safety settings appear to be enabled. In this post, you will learn why this flaw matters to your business, how to determine if you are affected, and what steps to take immediately to protect your operations and data.
Background & History
CVE-2026-44513 was publicly disclosed on May 14, 2026, and affects the Diffusers library, a widely used Python package for diffusion-based AI models maintained by Hugging Face. The vulnerability carries a CVSS v3.1 base score of 8.8, classifying it as High severity. It is a remote code execution (RCE) flaw stemming from a bypass of the trust_remote_code security mechanism in the DiffusionPipeline.from_pretrained() function. The issue was reported by security researchers who identified that the safety check was incorrectly placed in the code, allowing malicious repositories to execute code even when users explicitly disabled remote code trust. The fix was released in Diffusers version 0.38.0 on the same day as disclosure, following coordination between Hugging Face and the security community.
What This Means for Your Business
This vulnerability poses direct risks to your business operations, data integrity, and regulatory compliance. If an attacker exploits CVE-2026-44513, they can silently execute malicious code on any system that loads a compromised AI model. This could lead to data theft, unauthorized access to internal networks, or disruption of critical AI-driven services such as customer chatbots, image generation pipelines, or predictive analytics platforms. For organizations in regulated industries—such as finance, healthcare, or government—this flaw could trigger compliance violations under frameworks like HIPAA, PCI DSS, or NIST, especially if sensitive data is exposed or systems are compromised without detection. Beyond technical impact, successful exploitation could damage your reputation with customers and partners who rely on your AI systems to be secure and trustworthy. Because the attack requires only that a user load a malicious model repository—often through routine development or deployment workflows—the risk extends to any team using Diffusers without strict repository validation controls.
Real-World Examples
Regional Bank Using AI for Fraud Detection: A mid-sized bank employs Diffusers-based models to analyze transaction patterns. A developer loads a community-hosted model from Hugging Face Hub without verifying its source. The model contains malicious code that exfiltrates customer transaction data to an external server, triggering a regulatory investigation and customer notification requirements.
Healthcare Startup Deploying Diagnostic Imaging Tools: A digital health company integrates a Diffusers pipeline into its diagnostic imaging platform. An attacker uploads a crafted model to a public repository that the startup’s engineering team trusts. Upon loading, the model executes code that installs a backdoor, allowing persistent access to patient records and violating HIPAA safeguards.
E-Commerce Platform with Personalized Recommendations: An online retailer uses Diffusers to power its product recommendation engine. A compromised model repository leads to arbitrary code execution on the recommendation server, enabling attackers to manipulate product rankings or inject fraudulent affiliate links, resulting in revenue loss and brand erosion.
University Research Lab Running Generative AI Experiments: A research institution downloads a popular diffusion model for academic experiments. The model’s repository includes a malicious payload that mines cryptocurrency on lab servers, consuming computational resources and delaying critical research projects while incurring unexpected cloud infrastructure costs.
Am I Affected?
You are likely affected by CVE-2026-44513 if any of the following apply to your environment:
- You are running the Python
diffuserspackage version 0.37.0 or earlier. - Your AI/ML pipelines call
DiffusionPipeline.from_pretrained()with thecustom_pipelineargument pointing to a Hugging Face Hub repository. - Your team loads local model snapshots that contain custom Python files (e.g.,
pipeline.py,unet/*.py) referenced inmodel_index.json. - You use Diffusers in any capacity without explicitly validating the source and contents of every model repository before loading.
- Your MLOps or data science workflows automatically pull models from Hugging Face Hub without integrity checks or allowlisting.
Key Takeaways
- CVE-2026-44513 enables silent remote code execution in systems using vulnerable versions of the Diffusers library.
- The flaw bypasses safety settings, meaning even cautious configurations may not protect your environment.
- Business impacts include data breaches, service disruption, compliance violations, and reputational harm.
- Immediate patching to Diffusers version 0.38.0 or later is the only complete remediation.
- Until patched, restrict model loading to fully trusted, audited repositories and inspect local snapshots for unexpected Python files.
Call to Action
Don’t wait for an incident to assess your exposure. IntegSec specializes in penetration testing for AI/ML infrastructure and can help you identify vulnerabilities like CVE-2026-44513 before attackers do. Contact us today for a comprehensive security assessment and a tailored roadmap to reduce your cybersecurity risk. Visit https://integsec.com to get started.
Technical Appendix
A — Technical Analysis
CVE-2026-44513 is a code injection vulnerability in the Hugging Face diffusers Python package (versions prior to 0.38.0). The root cause lies in the implementation of the trust_remote_code gate within DiffusionPipeline.download(), rather than at the actual dynamic module loading site (get_cached_module_file in dynamic_modules_utils.py). This design flaw allows three distinct attack variants to bypass the security check: (1) cross-repo custom_pipeline loads, where the gate evaluates the wrong repository; (2) local snapshot paths combined with Hub-based custom_pipeline arguments, which skip download() entirely; and (3) local snapshots containing custom component files referenced in model_index.json. The attack vector is network-based (AV:N), with low complexity (AC:L), no privileges required (PR:N), and user interaction needed (UI:R)—typically a developer loading a model. The CVSS v3.1 vector is CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:H/A:H, yielding a base score of 8.8. This maps to CWE-94 (Improper Control of Generation of Code). The official NVD entry is available at https://nvd.nist.gov/vuln/detail/CVE-2026-44513.
B — Detection & Verification
Version Enumeration:
Run the following in your Python environment to check the installed diffusers version:
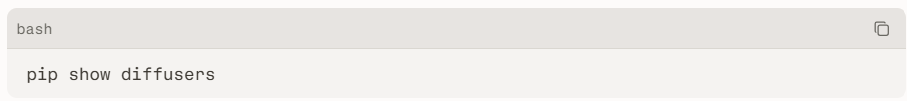
If the version is < 0.38.0, the system is vulnerable.
Scanner Signatures:
Software composition analysis (SCA) tools such as Snyk, Dependabot, or GitLab Dependency Scanning will flag CVE-2026-44513 when diffusers<0.38.0 is detected in requirements.txt, pyproject.toml, or lock files.
Log Indicators:
Monitor for calls to DiffusionPipeline.from_pretrained() with custom_pipeline arguments pointing to external repositories, especially those not on an allowlist. Unusual subprocess spawning or network connections from AI inference services may indicate exploitation.
Behavioral Anomalies:
Look for unexpected Python file execution in model directories (e.g., None.py, pipeline.py, or files under unet/, scheduler/). Network egress from model-loading processes to unknown IPs is a strong exploitation indicator.
Network Exploitation Indicators:
Outbound connections from AI workloads to Hugging Face Hub repositories not previously accessed, or to non-Hugging Face domains during model loading, should be investigated.
C — Mitigation & Remediation
1. Immediate (0–24h):
- Upgrade
diffusersto version 0.38.0 or later: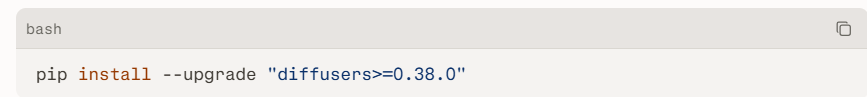
- If upgrading is not immediately possible, halt all
from_pretrained()calls that usecustom_pipelinewith external repositories or local snapshots containing custom Python files. - Audit all model repositories currently in use and restrict access to only those that have been manually reviewed and allowlisted.
2. Short-term (1–7d):
- Implement repository allowlisting in MLOps pipelines to prevent loading of unvetted models.
- Add pre-commit or CI checks that scan for
diffusersversion constraints and block merges if<0.38.0is detected. - Review logs for any historical
from_pretrained()calls with suspiciouscustom_pipelinepaths or local snapshots.
3. Long-term (ongoing):
- Enforce supply chain security practices for AI models, including cryptographic signing of trusted repositories and integrity verification before loading.
- Integrate SCA tools into CI/CD to automatically detect and block vulnerable dependencies.
- Conduct regular penetration tests focused on AI/ML infrastructure to identify similar logic flaws in custom pipelines or model loaders.
Official Vendor Patch:
The definitive fix is available in diffusers v0.38.0 via PR #13448. The patch relocates the trust_remote_code enforcement to get_cached_module_file, ensuring all dynamic module loads—local, remote, or hybrid—are properly gated.
Interim Mitigations (if patching is delayed):
- Never pass
custom_pipeline=pointing to a Hub repository different from the primarypretrained_model_name_or_pathwithout auditing itspipeline.py. - Before loading local snapshots, inspect the directory tree for unexpected
.pyfiles, particularly under component subdirectories (unet/,scheduler/, etc.). - Run model-loading processes in isolated containers with minimal privileges and network egress restrictions.
D — Best Practices
- Enforce strict allowlisting of Hugging Face repositories and local model paths used in production AI pipelines.
- Integrate software composition analysis (SCA) into CI/CD to automatically detect and block vulnerable
diffusersversions. - Isolate model-loading workloads in sandboxed environments with restricted network and filesystem access.
- Require manual review and signing of all custom pipeline code before it is permitted in enterprise AI workflows.
- Conduct regular threat modeling sessions focused on AI supply chain risks, including model repository trust boundaries.
Leave Comment