
CVE-2026-33264: Apache Airflow Unsafe Deserialization Bug - What It Means for Your Business and How to Respond
Introduction
CVE-2026-33264 is a critical security vulnerability in Apache Airflow, the workflow orchestration platform many organizations use to automate data pipelines, analytics, cloud operations, and business processes. If your organization operates Airflow versions earlier than 3.3.0, this issue could allow a malicious or insufficiently trusted workflow author to execute code within core Airflow services.
The business concern is not simply that a workflow can fail. A successful compromise could give an attacker access to sensitive data flows, automation credentials, cloud-connected systems, and production workloads that depend on Airflow scheduling. Organizations in the United States and Canada should treat this as a priority where Airflow supports regulated data, customer-facing services, financial reporting, healthcare operations, or critical internal automation.
This post explains the vulnerability in business terms, outlines practical exposure scenarios, helps you determine whether you may be affected, and provides technical guidance for security and operations teams.
S1 — Background & History
Apache Airflow disclosed CVE-2026-33264 on July 7, 2026. The issue affects Apache Airflow versions earlier than 3.3.0 and involves the way the platform processes certain serialized workflow definitions, known as directed acyclic graphs or DAGs. Apache identified the issue as an unsafe handling of untrusted serialized data, which can allow code supplied through a workflow definition to run in privileged Airflow services.
The advisory credits Ziyu Lin, intadd, and K as finders, with bugbunny.ai identified as the supporting tool. Apache developers Amogh Desai and Jarek Potiuk are credited for remediation work.lists.apache
CISA’s Authorized Data Publisher assessment assigns CVE-2026-33264 a Critical 9.8 out of 10 score under the Common Vulnerability Scoring System. The NVD lists the weakness as CWE-502, Deserialization of Untrusted Data. Apache’s remediation is available in apache-airflow version 3.3.0 and later.
S2 — What This Means for Your Business
If you use a vulnerable Airflow deployment, this issue can undermine a key security assumption: that the people who create data workflows do not automatically receive the same level of system access as the services that run them. In a successful attack, a malicious workflow author could move from submitting workflow content to running code in Airflow’s scheduler or application programming interface server processes.
For your operations, that can mean disrupted pipelines, failed reporting, delayed data deliveries, or manipulation of scheduled tasks. Airflow often sits at the center of business automation, so an incident may cascade into business intelligence, billing, customer communications, supply chain coordination, and cloud operations.
For your data, a compromised Airflow control plane may expose credentials, connection configurations, environment variables, workflow code, logs, and data accessible to Airflow’s service accounts. The practical impact depends on the permissions assigned to those accounts and on how broadly Airflow is connected across your environment.
For your reputation and compliance posture, a security incident involving regulated personal information, financial data, or health information may trigger contractual notification obligations, regulatory review, incident-response costs, and loss of customer confidence. The highest risk exists where untrusted or broadly distributed users can contribute DAGs, or where access governance around workflow repositories and deployment processes is weak.
S3 — Real-World Examples
Regional Bank Data Operations: A regional bank uses Airflow to coordinate anti-money-laundering analytics, daily account reporting, and data transfers between internal systems. If an unauthorized party can introduce a malicious workflow, they may gain access to sensitive processing infrastructure, creating operational disruption and potential exposure of customer information.
Mid-Market Healthcare Provider: A healthcare organization relies on Airflow for data warehouse refreshes and claims-processing integrations. A compromise could interrupt time-sensitive reporting and create access paths to systems containing protected health information, requiring a careful legal, security, and privacy assessment.
North American Retailer: A retailer uses Airflow to synchronize inventory, order, pricing, and marketing data across cloud platforms. An attacker who compromises the workflow environment could alter scheduled jobs, interrupt fulfillment data, or access cloud credentials that support broader business systems.
Large Software-as-a-Service Provider: A software provider allows multiple engineering teams to contribute workflow definitions to a shared Airflow platform. Without firm separation between workflow authors and high-privilege Airflow services, one compromised developer account or malicious contribution could become a platform-wide control-plane incident rather than a contained application issue.
S4 — Am I Affected?
- You are running Apache Airflow earlier than version 3.3.0, including any supported or internally maintained deployment that uses the
apache-airflowpackage below 3.3.0. - You operate Airflow Scheduler or API Server processes that load serialized DAGs.
- You allow multiple developers, data engineers, contractors, partners, or business units to submit or modify DAG definitions.
- You use shared repositories, automated deployment pipelines, or third-party packages for workflow code without strong change controls.
- You rely on Airflow service accounts with access to cloud resources, databases, secrets, customer data, or production environments.
- You have configured broad deserialization class permissions or permissive regular expressions for Airflow’s deserialization settings.
- You are likely not affected by this specific vulnerability if every Airflow deployment is confirmed at version 3.3.0 or later and the upgrade was completed successfully.
Key Takeaways
- CVE-2026-33264 affects Apache Airflow versions earlier than 3.3.0 and can permit code execution through unsafe handling of serialized workflow content.
- The issue is especially consequential when DAG authors are less trusted than the administrators and service accounts operating the Airflow platform.
- A successful compromise can disrupt business automation and may expose credentials, connected systems, data pipelines, and production resources.
- Upgrading to Apache Airflow 3.3.0 or later is the primary remediation recommended by Apache.lists.apache+1
- Restricting the allowed deserialization classes is a valuable defense-in-depth step for organizations that cannot fully trust every workflow author.
Call to Action
CVE-2026-33264 is a reminder that workflow orchestration platforms are high-value control points, not just back-office tools. IntegSec can help you assess Airflow exposure, test access boundaries, validate cloud and credential segmentation, and prioritize remediation based on the systems your workflows can reach. A focused penetration test can identify the gaps that a version upgrade alone may not address. Contact IntegSec to strengthen your Airflow security posture and reduce cybersecurity risk across your automation environment.
TECHNICAL APPENDIX
A — Technical Analysis
CVE-2026-33264 is an insecure deserialization vulnerability in Apache Airflow’s serialized DAG processing path. The root cause is unrestricted import_string() processing of attacker-controlled class paths through BaseSerialization.deserialize(). When the Scheduler or API Server loads a serialized DAG containing a malicious trigger, the vulnerable path can cause attacker-selected code to execute in those higher-privilege Airflow processes. This violates Airflow’s intended security boundary, in which DAG-author code should not execute inside Scheduler or API Server processes.
The affected package is apache-airflow before version 3.3.0. The NVD identifies the weakness as CWE-502, Deserialization of Untrusted Data. The CISA-assigned CVSS v3.1 vector is CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H, scoring 9.8 Critical. This indicates a network-reachable issue with low attack complexity, no required privileges or user interaction in the scoring model, and high potential impact to confidentiality, integrity, and availability.
B — Detection & Verification
Verify deployed package versions and identify whether vulnerable Scheduler or API Server nodes process serialized DAGs. Do not test exploit payloads against production systems; validate versions, configuration, and deployment controls first.
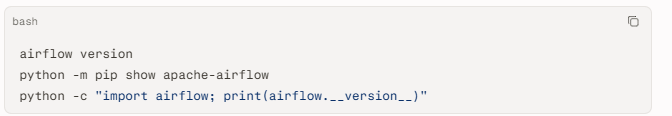
Version Verification: Systems reporting any Apache Airflow version below 3.3.0 should be treated as vulnerable until upgraded and validated. Containerized environments should be checked through image manifests, deployment specifications, and running pods rather than only a workstation dependency file.
Configuration Review: Inspect [core] allowed_deserialization_classes and allowed_deserialization_classes_regexp in the effective Airflow configuration. Broad wildcards, permissive regular expressions, or unnecessary classes increase exposure to unsafe deserialization paths.
Log Indicators: Review Scheduler and API Server logs for unexpected import failures, unusual trigger deserialization events, stack traces involving BaseSerialization.deserialize() or import_string(), and Python module names not approved for the environment.
Behavioral Indicators: Investigate unplanned child processes, unexpected outbound connections from Scheduler or API Server hosts, changes to DAG files, new environment variables, altered connection settings, or abnormal use of Airflow service-account credentials.
C — Mitigation & Remediation
- Immediate (0–24h): Identify every Apache Airflow deployment, including production, disaster recovery, development, and managed container environments. Confirm the effective installed version, locate Scheduler and API Server workloads, and determine which teams or automated processes can create, modify, approve, or deploy DAGs. Prioritize systems where DAG authors are not fully trusted or where Airflow service accounts can access sensitive data, cloud environments, or production infrastructure.
- Immediate (0–24h): Upgrade affected deployments to
apache-airflow3.3.0 or later using the official Apache release and your normal change-management process. Validate the deployed package or container image after rollout, restart affected Airflow services where required by your deployment model, and monitor job execution for compatibility issues. Apache identifies 3.3.0 as the patched version.lists.apache+1 - Short-term (1–7d): Where immediate patching is not feasible, restrict
[core] allowed_deserialization_classesto a narrow, documented allowlist required by approved workflows. Avoid broad patterns inallowed_deserialization_classes_regexp. Limit DAG author access, pause unreviewed DAG deployment pipelines, enforce peer review for workflow changes, and isolate Airflow service accounts from unnecessary cloud, database, and secret-management privileges. Apache specifically recommends a narrow allowlist as a defense-in-depth measure. - Short-term (1–7d): Hunt for indicators of compromise across DAG repositories, deployment pipelines, Scheduler logs, API Server logs, service-account activity, cloud audit trails, and outbound network telemetry. Review DAG changes submitted around the disclosure period and preserve relevant logs before retention limits remove evidence.
- Long-term (ongoing): Separate workflow-author permissions from platform-administration privileges. Apply least privilege to Airflow service identities, protect DAG repositories with branch controls and signed or reviewed changes, segment Airflow infrastructure, continuously inventory package versions, and include Airflow control-plane abuse scenarios in penetration tests and incident-response exercises.
D — Best Practices
- Upgrade Apache Airflow promptly and maintain an inventory that identifies every deployed Airflow version, container image, and environment.
- Treat DAG definitions as security-sensitive code, requiring protected repositories, peer review, restricted write access, and auditable deployment pipelines.
- Configure a minimal
allowed_deserialization_classesallowlist and avoid permissive regular-expression rules unless they are necessary and formally reviewed. - Limit Scheduler and API Server service-account permissions so a compromise cannot automatically reach all cloud services, databases, secrets, or production systems.
- Monitor Airflow control-plane logs, configuration changes, DAG deployments, process execution, and outbound connections for behavior inconsistent with approved workflow activity.
Leave Comment