
CVE-2026-31986: Apache OFBiz Hard-Coded Cryptographic Key Vulnerability - What It Means for Your Business and How to Respond
Introduction
CVE-2026-31986 represents a critical security flaw affecting Apache OFBiz, an open-source enterprise resource planning (ERP) platform used by thousands of organizations worldwide for accounting, customer relationship management, and supply chain operations. This vulnerability allows unauthenticated attackers to gain full administrative control over vulnerable systems and execute arbitrary code on your servers. If your organization runs Apache OFBiz for business operations, you face immediate risk of data breach, operational disruption, and regulatory non-compliance. This post explains what this vulnerability means for your business, how to determine whether you are affected, and the concrete steps you must take to protect your organization.novee
Background & History
CVE-2026-31986 was publicly disclosed on May 19, 2026, by security researchers Lidor Ben Shitrit and Assaf Levkovich. The vulnerability affects Apache OFBiz versions prior to 24.09.06, with the fixed version released as 24.09.06. While the National Vulnerability Database has not yet published an official CVSS score for this CVE, independent security assessments classify it as critical due to its remote code execution capability and zero authentication requirement. The flaw stems from hard-coded cryptographic signing keys that were inadvertently committed to the public Apache OFBiz source code repository. These default keys enable attackers to forge valid administrator authentication tokens without possessing legitimate credentials. Once administrative access is achieved through token forgery, attackers exploit template evaluation endpoints to execute arbitrary code on the underlying server, often requiring as few as two HTTP requests. The vulnerability type is classified as CWE-321: Use of Hard-coded Cryptographic Key, a well-documented weakness that has led to numerous high-profile breaches across the software industry.
What This Means for Your Business
This vulnerability poses severe operational, financial, and reputational risks to your organization. Apache OFBiz often serves as the backbone for critical business functions including financial transactions, customer data management, and inventory control. An attacker exploiting this flaw gains complete administrative control, enabling them to access sensitive financial records, customer personally identifiable information, proprietary business data, and intellectual property. The business impact extends far beyond immediate data exposure. Operational disruption is highly likely, as attackers can modify or delete critical business records, alter pricing and inventory data, or disable essential system functions entirely. Your organization faces significant compliance exposure under regulations such as PCI DSS for payment card data, GDPR for European customer information, HIPAA for healthcare data, and various state privacy laws in the United States and Canada. Regulatory fines for breaches involving unpatched critical vulnerabilities can reach millions of dollars, not including litigation costs, customer notification expenses, and credit monitoring services. Reputational damage compounds these costs, as customers and business partners lose confidence in your ability to protect their information. For publicly traded companies, disclosure of a breach stemming from a known, unpatched critical vulnerability can trigger shareholder lawsuits and securities regulatory scrutiny. The remote, unauthenticated nature of this exploit means attackers need no prior access to your network, dramatically expanding your threat surface to include any internet-connected OFBiz instance.
Real-World Examples
Regional Manufacturing Company: A mid-sized manufacturer running Apache OFBiz for inventory and order management discovers attackers have altered pricing tables and shipped products at fraudulent discount rates. The breach results in six-figure revenue losses, customer chargeback disputes, and a three-week operational shutdown while forensic investigators rebuild compromised systems.novee
Healthcare Services Provider: A regional healthcare administrator using OFBiz for patient billing and scheduling experiences unauthorized access to protected health information. HIPAA violations trigger federal investigation, mandatory breach notifications to thousands of patients, and corrective action plans requiring ongoing third-party auditing.novee
E-Commerce Retailer: An online retailer's OFBiz-powered customer database is exfiltrated by attackers who forged administrative tokens. The breach exposes names, addresses, purchase histories, and partial payment information for over 100,000 customers, prompting class-action litigation and state attorney general investigations.novee
Financial Services Firm: A credit union leveraging OFBiz for member account management faces regulatory enforcement action after attackers modify account balances and transaction histories. State banking regulators impose operational restrictions, require independent security assessments, and mandate board-level oversight of cybersecurity remediation efforts.novee
Am I Affected?
You are at risk if any of the following conditions apply to your organization:
- You are running Apache OFBiz version 24.09.05 or earlier on any server in your environment.novee
- Your Apache OFBiz deployment has Single Sign-On (SSO) authentication enabled, which is the default configuration for most installations.novee
- You deployed Apache OFBiz using official distribution packages without modifying the default cryptographic key configurations.novee
- Your organization uses Apache OFBiz for any business-critical function including accounting, CRM, inventory management, or order processing.novee
- You cannot confirm with certainty that all OFBiz instances have been upgraded to version 24.09.06 or later.novee
Key Takeaways
- CVE-2026-31986 allows unauthenticated attackers to forge administrator tokens and execute arbitrary code on Apache OFBiz servers.novee
- Organizations running OFBiz versions prior to 24.09.06 face immediate risk of data breach and operational disruption.novee
- Business impacts include regulatory fines, litigation costs, reputational damage, and potential loss of customer trust.novee
- Patching to version 24.09.06 is the only complete remediation; interim mitigations provide limited protection.novee
- Engage qualified cybersecurity professionals to assess exposure, verify patching, and conduct penetration testing.novee
Call to Action
Your organization cannot afford to wait. CVE-2026-31986 represents an active, exploitable threat that demands immediate attention from leadership and technical teams alike. IntegSec specializes in helping businesses across the United States and Canada identify, validate, and remediate critical vulnerabilities like this one through comprehensive penetration testing and cybersecurity risk assessments. Our certified security engineers will verify your OFBiz deployment status, test for exploitation indicators, and provide actionable remediation guidance tailored to your specific environment. Contact IntegSec today at https://integsec.com to schedule your assessment and take decisive action against this and other critical threats facing your business.novee
TECHNICAL APPENDIX
A — Technical Analysis
CVE-2026-31986 originates from hard-coded cryptographic signing keys embedded within the Apache OFBiz Single Sign-On (SSO) authentication module and signing mechanism. The root cause is CWE-321: Use of Hard-coded Cryptographic Key, where default cryptographic keys were committed to the public source code repository and remain unchanged in production deployments. The affected component is the SSO token generation and validation subsystem, which uses these static keys to sign and verify authentication tokens. The attack vector is network-based (AV:N), requiring no authentication (PR:N) and no user interaction (UI:N), with low attack complexity (AC:L). An unauthenticated remote attacker can forge valid administrator SSO tokens using the known static secret keys, bypassing all authentication controls. Upon achieving authenticated administrative access, attackers exploit internal application features such as template evaluation endpoints to achieve remote code execution. The denylist filter restricting dangerous Java execution patterns was case-sensitive and checked narrow string signatures, allowing trivial bypass via alternate letter casing or alternative auto-imported classes. Exploitation requires as few as two HTTP GET requests. NVD reference is pending official publication; the CVE is tracked at cve.org under CVE-2026-31986.novee
B — Detection & Verification
Version Enumeration:
- Execute the following command on OFBiz application servers to identify the installed version:
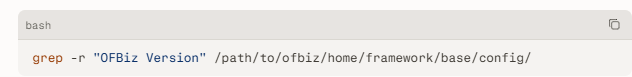
- Alternatively, access the OFBiz administrative interface and navigate to System > About to display the version number.novee
- Any version prior to 24.09.06 is vulnerable.novee
Scanner Signatures:
- Nessus plugin ID pending (monitor Tenable feed for CVE-2026-31986 signature).
- Qualys QID pending (check Qualys KnowledgeBase for Apache OFBiz hard-coded key detection).
- Rapid7 InsightVM: Monitor community exploit modules for OFBiz SSO token forgery indicators.novee
Log Indicators:
- Unusual SSO token generation events in OFBiz application logs, particularly tokens created without corresponding user authentication attempts.novee
- Administrative actions executed from unexpected IP addresses or during non-business hours.novee
- Template evaluation endpoint access patterns showing repeated requests with varying parameter casing.novee
Behavioral Anomalies:
- Sudden appearance of administrative users or sessions without corresponding HR onboarding or access request workflows.novee
- Configuration changes to critical business modules (pricing, inventory, user management) without change management tickets.novee
Network Exploitation Indicators:
- HTTP GET requests to OFBiz SSO endpoints containing unusually long or structured token parameters.novee
- Requests to template evaluation or expression parsing endpoints immediately following SSO authentication events.novee
- Outbound connections from OFBiz servers to unexpected external IPs following suspected exploitation windows.novee
C — Mitigation & Remediation
1. Immediate (0–24h):
- Isolate all Apache OFBiz instances from external network access if business continuity permits.novee
- Block external access to OFBiz SSO endpoints at the firewall or load balancer level.novee
- Review OFBiz application logs for indicators of compromise, focusing on administrative actions and SSO token events.novee
- Initiate incident response procedures if exploitation indicators are present; preserve forensic evidence.novee
2. Short-term (1–7d):
- Upgrade all Apache OFBiz instances to version 24.09.06 or later.novee
- If immediate patching is not feasible, disable SSO functionality in the OFBiz configuration:
- Edit
framework/security/config/security.properties - Set
sso.enabled=false - Restart OFBiz application servernovee
- Edit
- Regenerate all cryptographic keys used by OFBiz, including any custom keys beyond the default hard-coded values.novee
- Conduct full credential rotation for all administrative accounts.novee
3. Long-term (ongoing):
- Implement automated vulnerability scanning for all enterprise applications, with specific checks for hard-coded credentials and cryptographic weaknesses.novee
- Establish a software composition analysis (SCA) pipeline to detect hard-coded secrets in custom and open-source code before deployment.novee
- Require security review of all configuration files and deployment artifacts for hard-coded keys, passwords, or tokens.novee
- Integrate OFBiz into your organization's patch management program with defined SLAs for critical security updates.novee
- Conduct annual penetration testing focused on authentication bypass and token forgery attack vectors.novee
Official Vendor Patch: Apache OFBiz version 24.09.06 resolves this vulnerability by removing hard-coded cryptographic keys and requiring unique key generation during installation. Download the official patch from the Apache OFBiz distribution repository and follow vendor upgrade documentation.novee
Interim Mitigations for Unpatchable Environments:
- Disable SSO functionality entirely if business processes allow alternative authentication mechanisms.novee
- Implement network segmentation to restrict OFBiz access to trusted internal networks only.novee
- Deploy web application firewall rules to block requests matching known exploitation patterns for SSO token forgery.novee
- Enable enhanced logging and alerting on all OFBiz administrative functions.novee
D — Best Practices
- Never deploy software with default cryptographic keys; require unique key generation during installation and configuration.novee
- Implement secrets management solutions (such as HashiCorp Vault or AWS Secrets Manager) to store and rotate cryptographic keys securely.novee
- Conduct regular code reviews and static analysis scans to detect hard-coded credentials, keys, or tokens in application source code.novee
- Establish a vulnerability management program that prioritizes remediation based on exploitability, asset criticality, and business impact.novee
- Perform penetration testing annually, with specific focus on authentication mechanisms, token handling, and cryptographic implementations
Leave Comment